Production-Tested Compliance Resources, Available on Demand
Our Academy shows teams how to build secure, automated hybrid infrastructure. Our Toolkit gives them everything they need to keep it that way.
Our Unique Approach
Cyber Rapport Academy is strengthening cybersecurity resilience within the U.S. financial services and insurance sector through the Secure Hybrid Compliance Framework, a structured approach designed for hybrid cloud and endpoint environments used by regulated organizations.
We deliver the Framework through four integrated components:
1. Production implementation with early-adopter organizations,
2. A subscription-based Secure Hybrid Compliance Toolkit containing reusable Terraform modules and PowerShell remediation workflows,
3. The Cyber Rapport Academy, which offers hands-on instruction for mid-to-senior cybersecurity professionals, and
4. A Security Change Enablement discipline that operates across all components, equipping technical teams to build internal support, measure true adoption, and sustain implemented controls within their organizations.

Our Curriculum
The Cyber Rapport Academy curriculum translates the Secure Hybrid Compliance Framework into practical, hands-on instruction for mid-to-senior professionals working in cloud infrastructure or security operations within regulated organizations.
Each of the seven modules combines focused instruction with a hands-on lab that produces resources participants can adapt to their own environments. The course culminates in an integrated capstone that connects technical implementation with organizational adoption.
01
Module 1
Foundations of Cyber Rapport & Secure Hybrid Cloud for Regulated Environments
Establishes the risk profile of financial services and insurance environments, maps practical controls to NIST CSF 2.0 and CISA guidance, and introduces the zero trust and Cyber Rapport principles that underpin the full curriculum.
02
Module 2
Secure Infrastructure-as-Code with Terraform & Packer
Teaches participants to design and deploy reusable, secure-by-default Terraform modules, manage infrastructure through Git-based pipelines with policy gates, and create hardened golden images using Packer.
03
Module 3
Automated Vulnerability & Patch Management Pipelines
Covers the design of end-to-end automated vulnerability detection and remediation pipelines, including risk-based prioritization and the sustained achievement of high patch compliance across third-party applications.
04
Module 4
Zero Trust Identity & Access Controls
Guides participants through the design and implementation of Microsoft Entra ID Conditional Access policies and Privileged Identity Management for just-in-time access within regulated hybrid environments.
05
Module 5
Endpoint, VDI & Mobile Security at Scale
Addresses the secure provisioning and management of large fleets of endpoints, Azure Virtual Desktop environments, and mobile devices using Microsoft Defender for Endpoint and Intune and SCCM co-management patterns.
06
Module 6
Operationalizing Continuous Compliance
Establishes the monitoring, drift detection, automated remediation, and documentation processes required to maintain cybersecurity controls within regulated production environments on an ongoing basis.
07
Module 7
Cyber Rapport: Security Change Enablement & Business Relationship Management
Teaches participants to map stakeholder landscapes, recruit internal change champions, apply friction engineering, measure true control adoption, and manage exceptions before resistance leads to bypass or rollback.
08
Module 8
Integrated Capstone: 90-Day Implementation Roadmap
Participants develop a personalized 90-day implementation roadmap combining Toolkit components with a full Cyber Rapport adoption plan and a change management and knowledge base strategy suited to their own organization.
Security Change Enablement and Business Relationship Management
Deploying a security control and sustaining its effectiveness are two distinct challenges: Mapping and Implementation.
Cyber Rapport Academy addresses both.
1. Mapping
The Cyber Rapport methodology begins by mapping the stakeholders whose support will determine how a change is received, then builds those relationships before implementation begins and communicates the operational purpose of the control in terms that affected employees can act on.
Internal champions are recruited to reinforce the change within their teams and provide feedback on adoption problems before those problems lead to exceptions or rollback.
2. Implementation
Where new requirements introduce friction that cannot be eliminated, implementation teams are guided to pair that friction with a visible workflow improvement that gives affected users a reason to engage.
Because adoption is measured separately from deployment, organizations gain a clear picture of whether controls are functioning as intended, not simply whether they have been switched on.
These practices are embedded across the Framework: they guide stakeholder engagement during production excellence engagements, are built into the Toolkit's implementation resources, and are taught in depth through Module 7 of the Academy curriculum and applied within each participant's 90-day implementation roadmap.
The Secure Hybrid Compliance Toolkit
Financial services and insurance organizations operating in hybrid cloud and endpoint environments face persistent challenges in maintaining approved security configurations and sustaining compliance after controls are deployed.
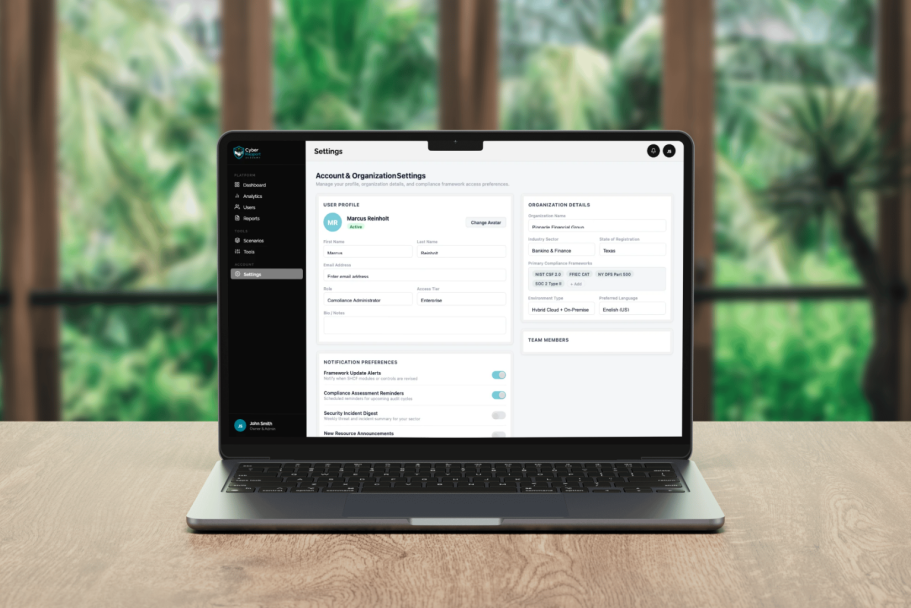
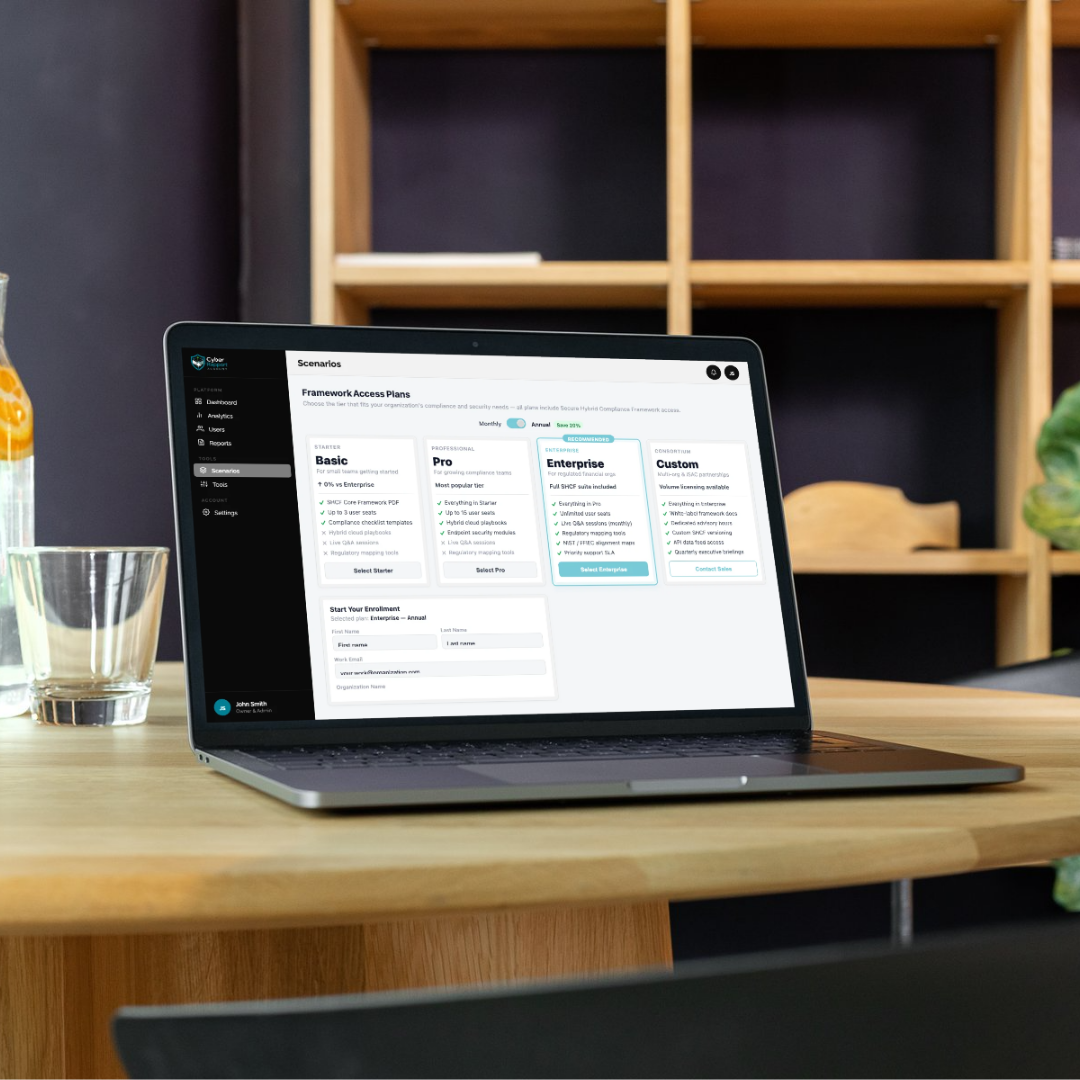
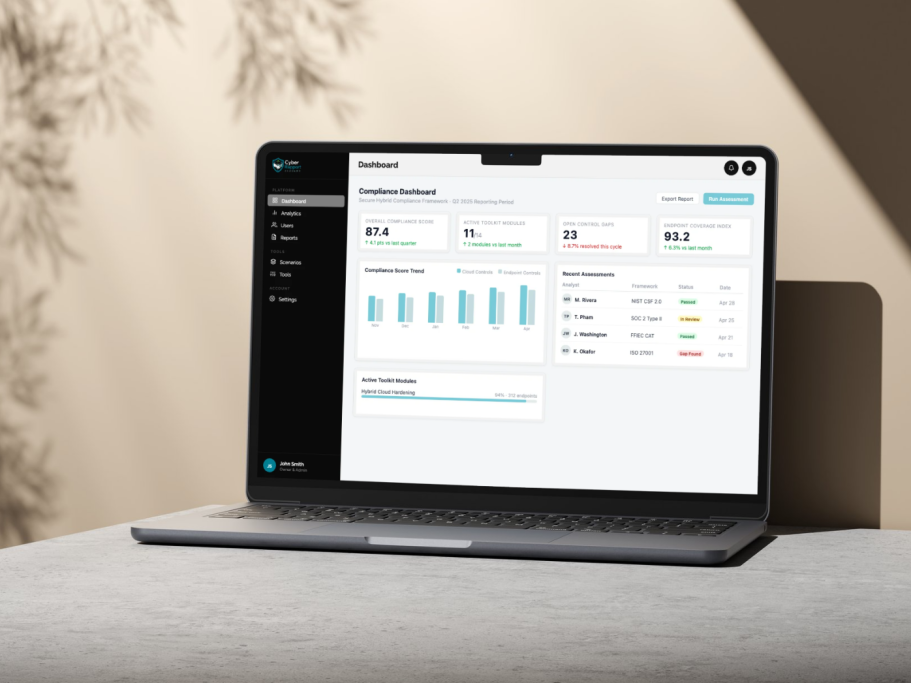
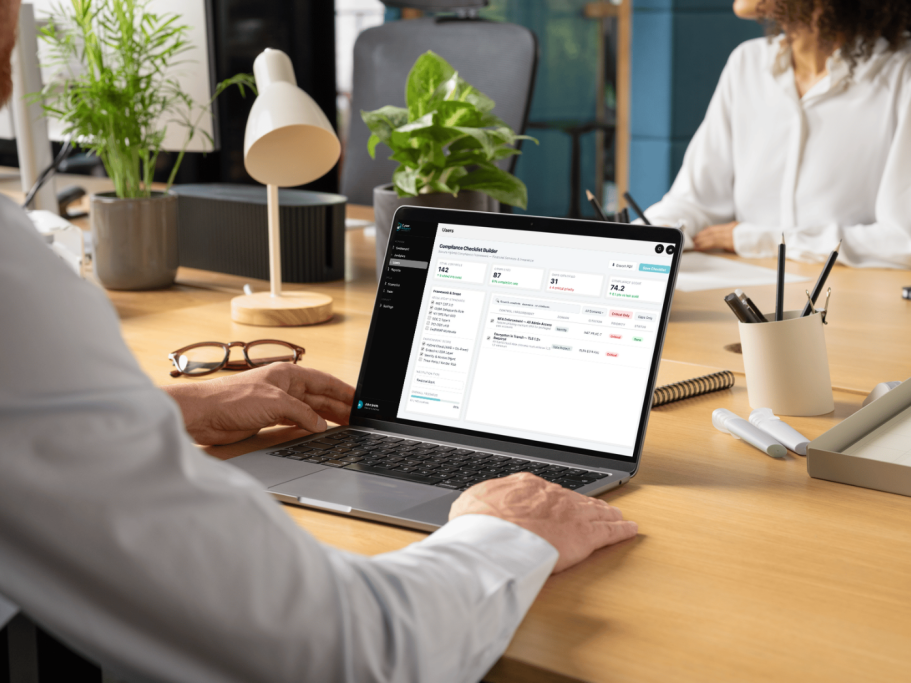
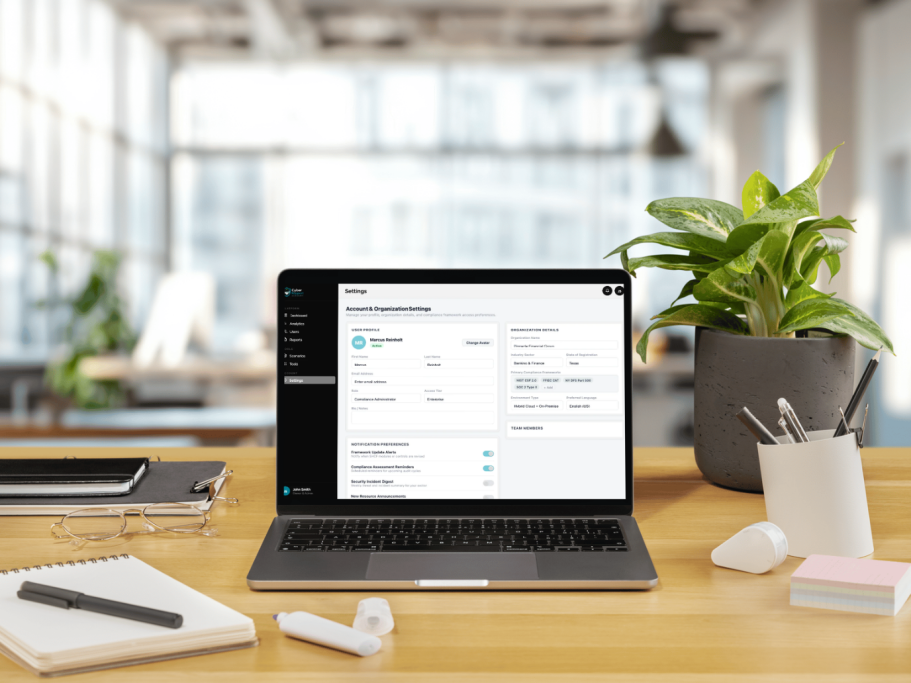
The Secure Hybrid Compliance Toolkit is a subscription-based digital platform housing version-controlled Terraform modules, hardened Packer images, PowerShell runbooks, and policy gates, all mapped to NIST Cybersecurity Framework 2.0 and CISA Cross-Sector Cybersecurity Performance Goals, enabling regulated organizations to deploy and maintain approved configurations within their own environments.
Standard and Enterprise Managed Continuous Compliance subscription tiers provide access to both technical resources and Cyber Rapport adoption tools, including stakeholder identification support, adoption dashboards, and exception-management workflows.
"Too many regulated organizations deploy security controls that don't survive first contact with the people who have to use them. I founded Cyber Rapport Academy to close the gap between technical implementation and sustained adoption."
SEAN EATCH - FOUNDER & CEO
Contact Us
Have questions about how Cyber Rapport Academy can strengthen cybersecurity resilience within your financial services or insurance organization?
Reach out to us by leaving your name and e-mail address or submit an inquiry through our contact page.